


The applications your people use
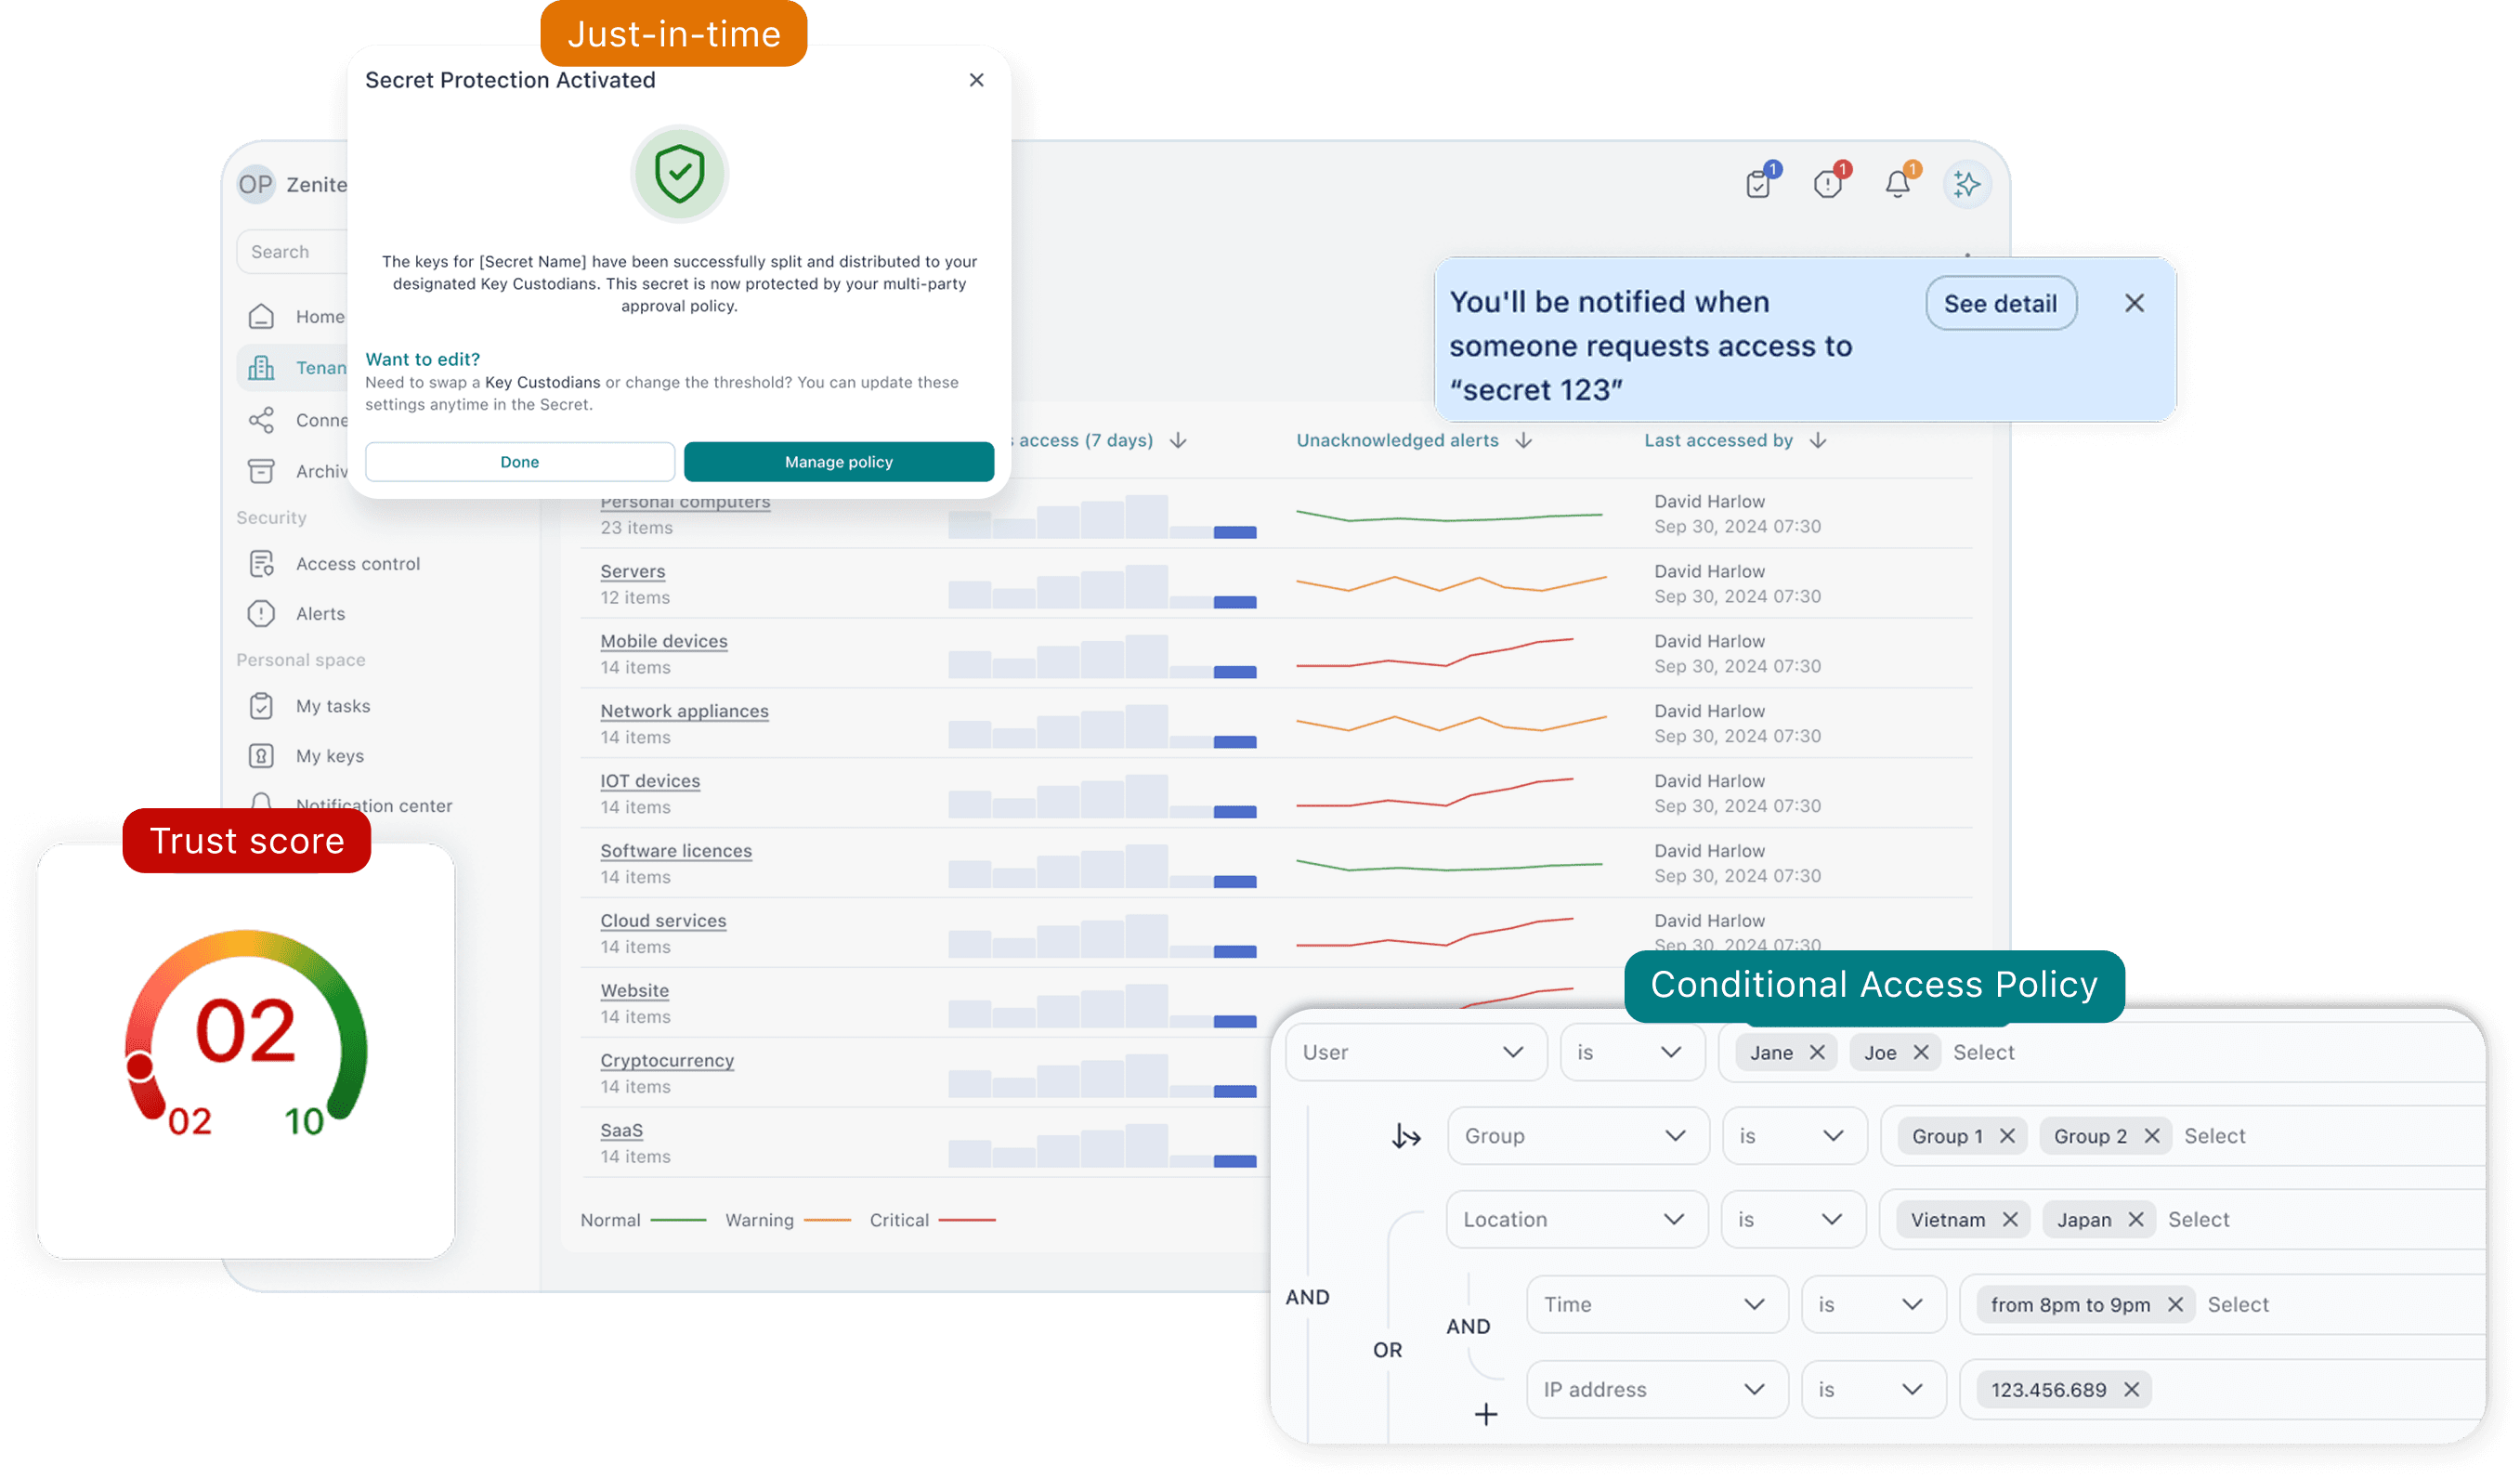
Privileged admin consoles, internal business applications, and infrastructure portals delivered directly to individual operators through identity-driven, just-in-time access.
A locked down architecture for the passwords people use, the secrets your code runs on, and the keys your agents never get to hold. Every request flows through Zero Trust software-defined perimeter which analyzes the requester, the resource, and the live risk of the session.
Trusted by security and IT teams at


Why your organization needs a key management system
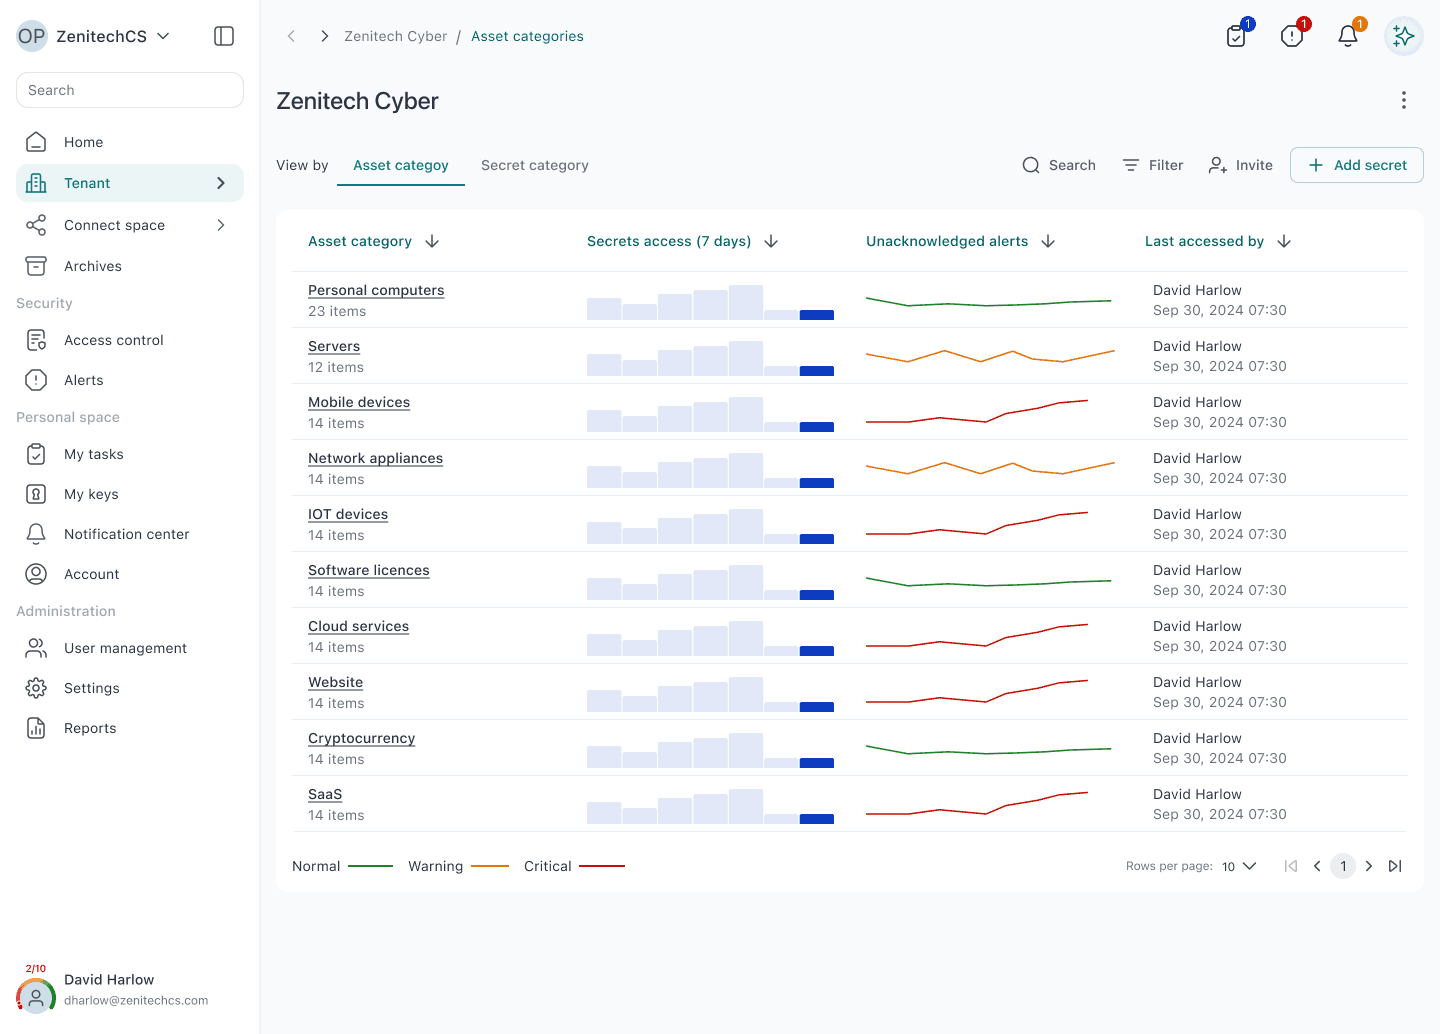
Secrets are scattered everywhere: hardcoded in code, shared in Slack and email, and left unrotated for years. They’re duplicated across vaults, .env files, and CI configs with no unified visibility or control. This sprawl is the broader security challenge you can’t ignore.
Privileged admin consoles, internal business applications, and infrastructure portals delivered directly to individual operators through identity-driven, just-in-time access.

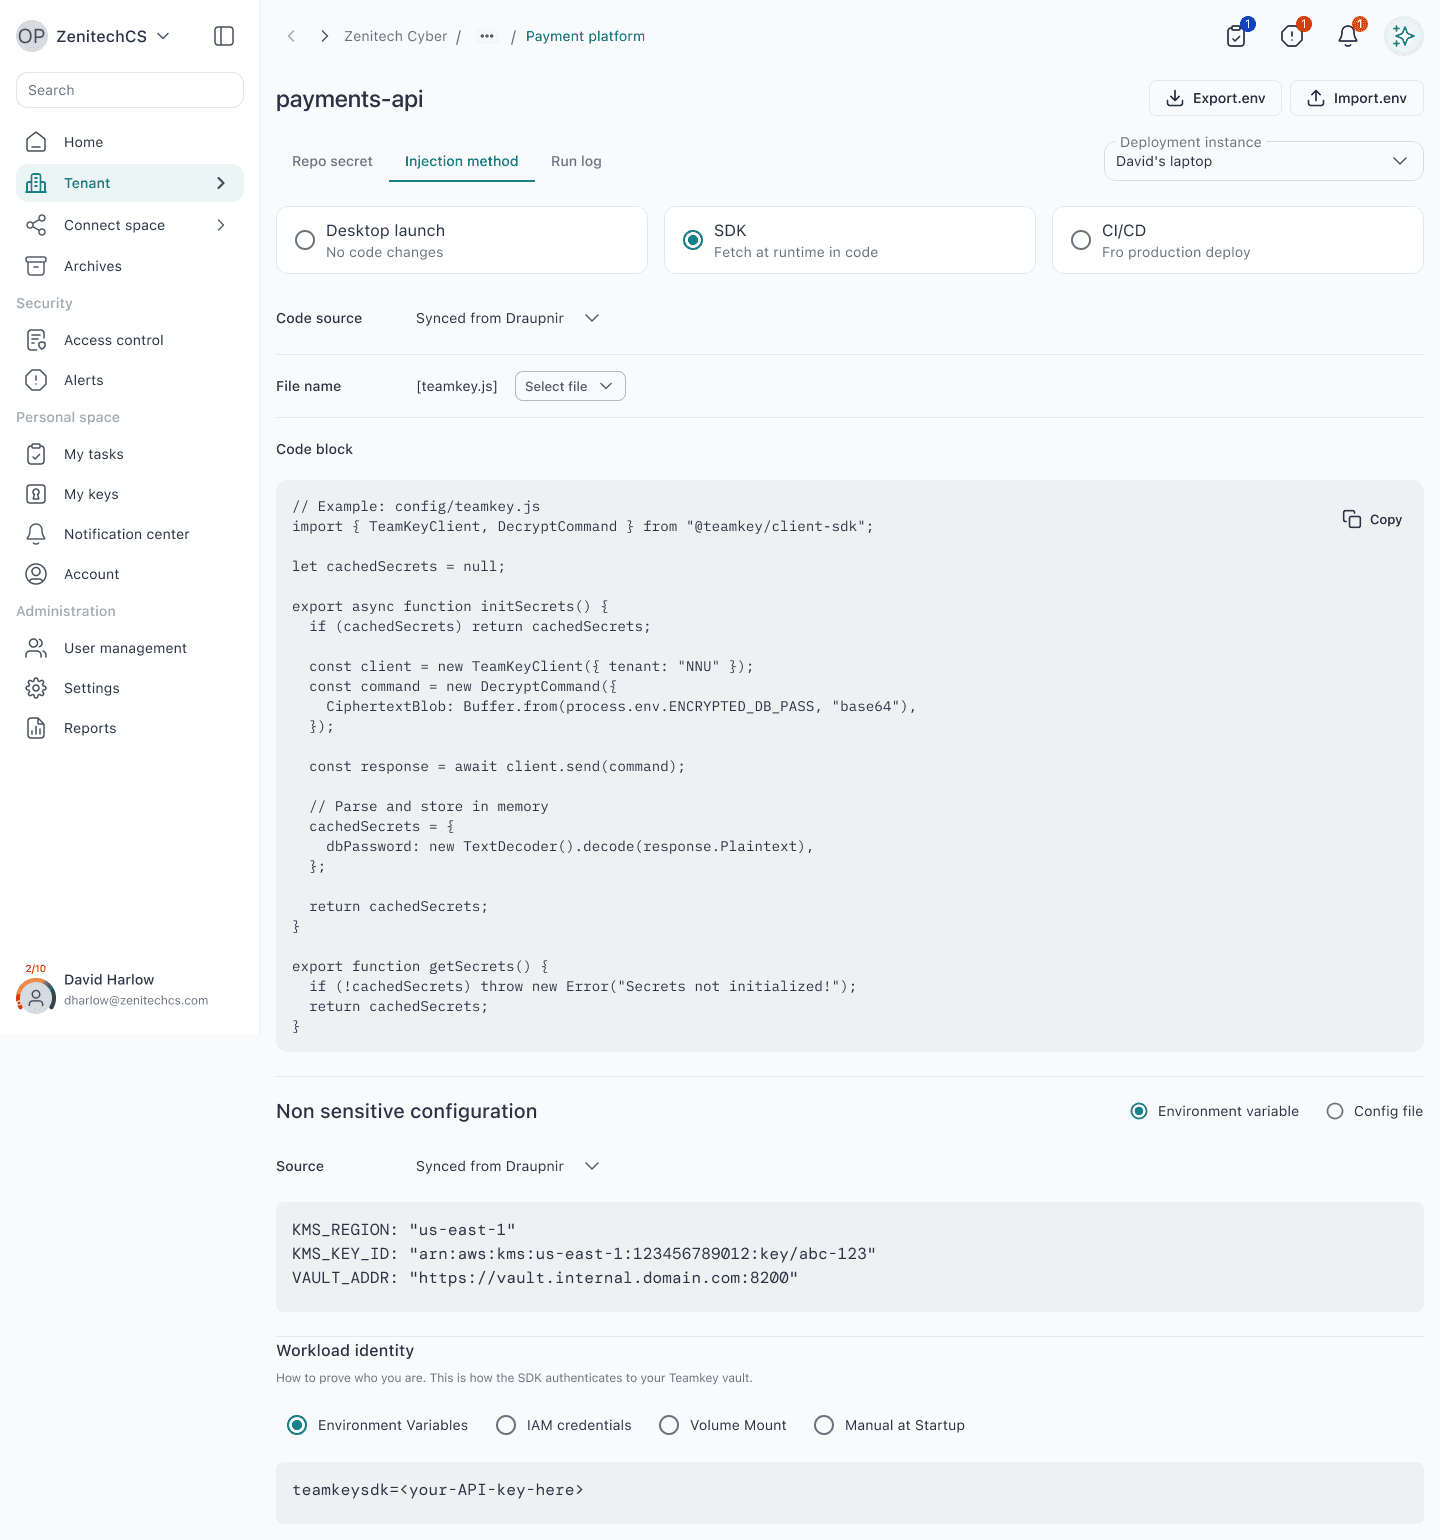
Stateless application instances, distributed brokers, and integration clients dynamically provisioned with ephemeral credentials injected into runtime memory—eliminating static secrets from the entire source tree.

Enterprise databases, session memory stores, and third-party API credentials accessed dynamically across agent orchestration layers, model context windows, and tool execution environments.
About our product
Explore the core capabilities that power TeamKey's zero-trust architecture.
Every credential, key, token, and certificate governed by a Zero Trust SDP vault—invisible across the public and corporate network by default. Access to cryptographic keys is dynamically brokered through context-aware SDP controllers, binding every request to continuous device posture, cryptographic workload identity, and tenant policy before an encrypted micro-tunnel to the vault is ever established.
Secrets reach the process, container, or pipeline that needs them at the moment of use — as environment variables, over stdin, into a RAM-backed file, or through the SDK. Never written to disk, never in shell history, never baked into an image. Leased, renewed, and revoked the instant authorization changes.
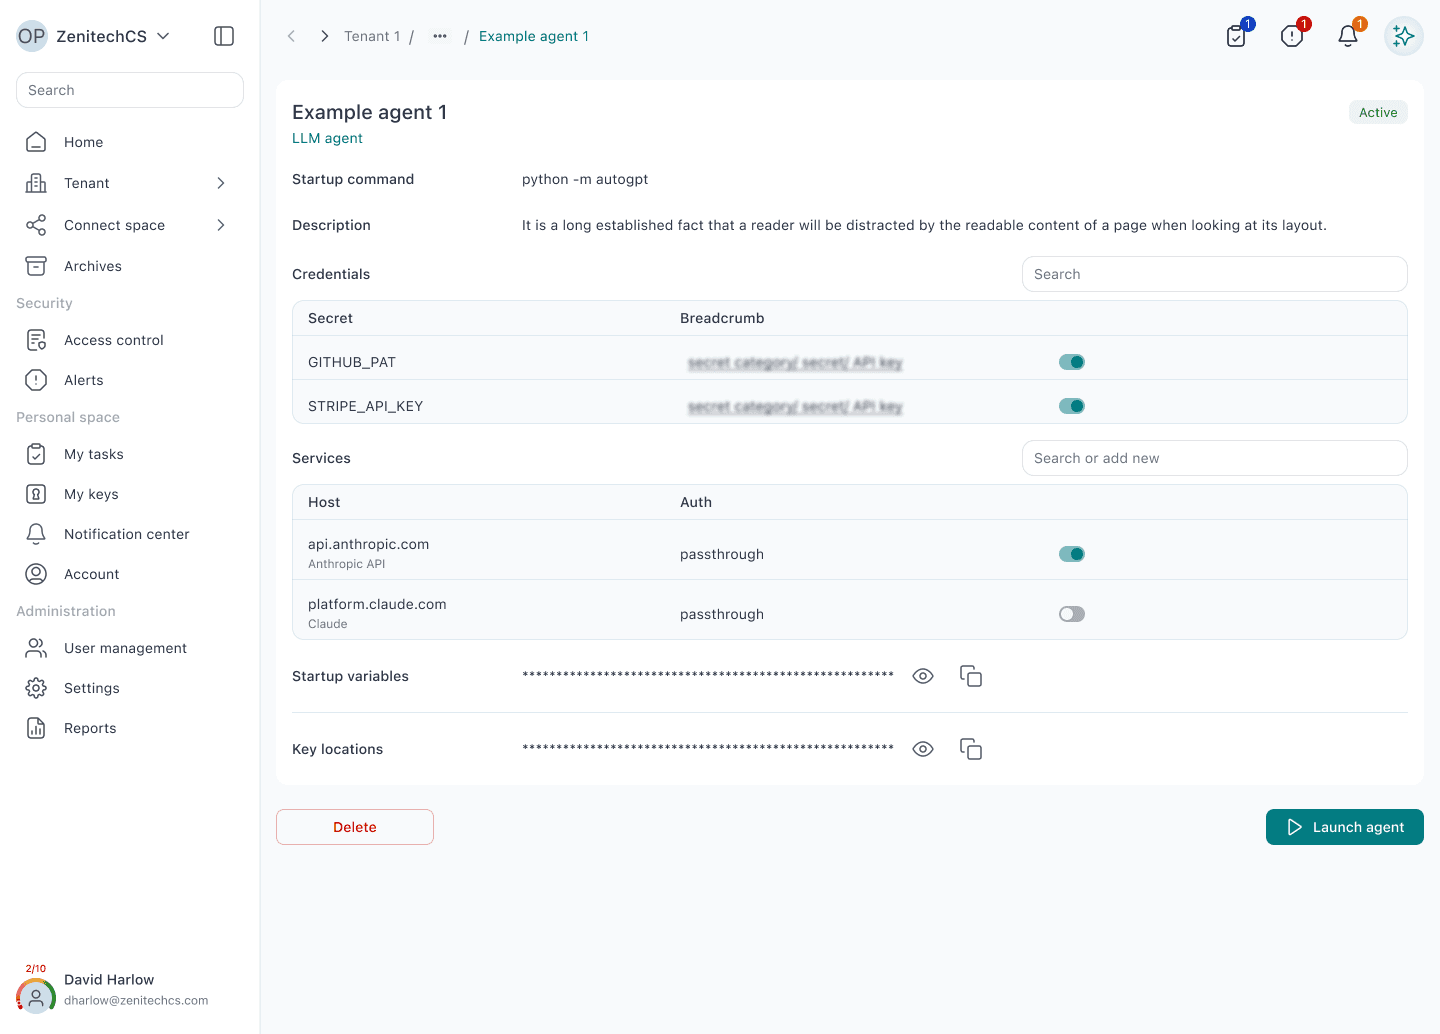
Your autonomous agents operate with cryptographic workload identities, authorized for specific tools without ever holding raw credentials or session tokens. TeamKey sits directly in the execution path as an intelligent control plane: it intercepts every tool-call and downstream API request, evaluates prompt intent against semantic guardrails, and routes anomalous or high-impact actions to human-in-the-loop approval workflows. Only upon explicit policy authorization does TeamKey sign the payload with just-in-time credentials.
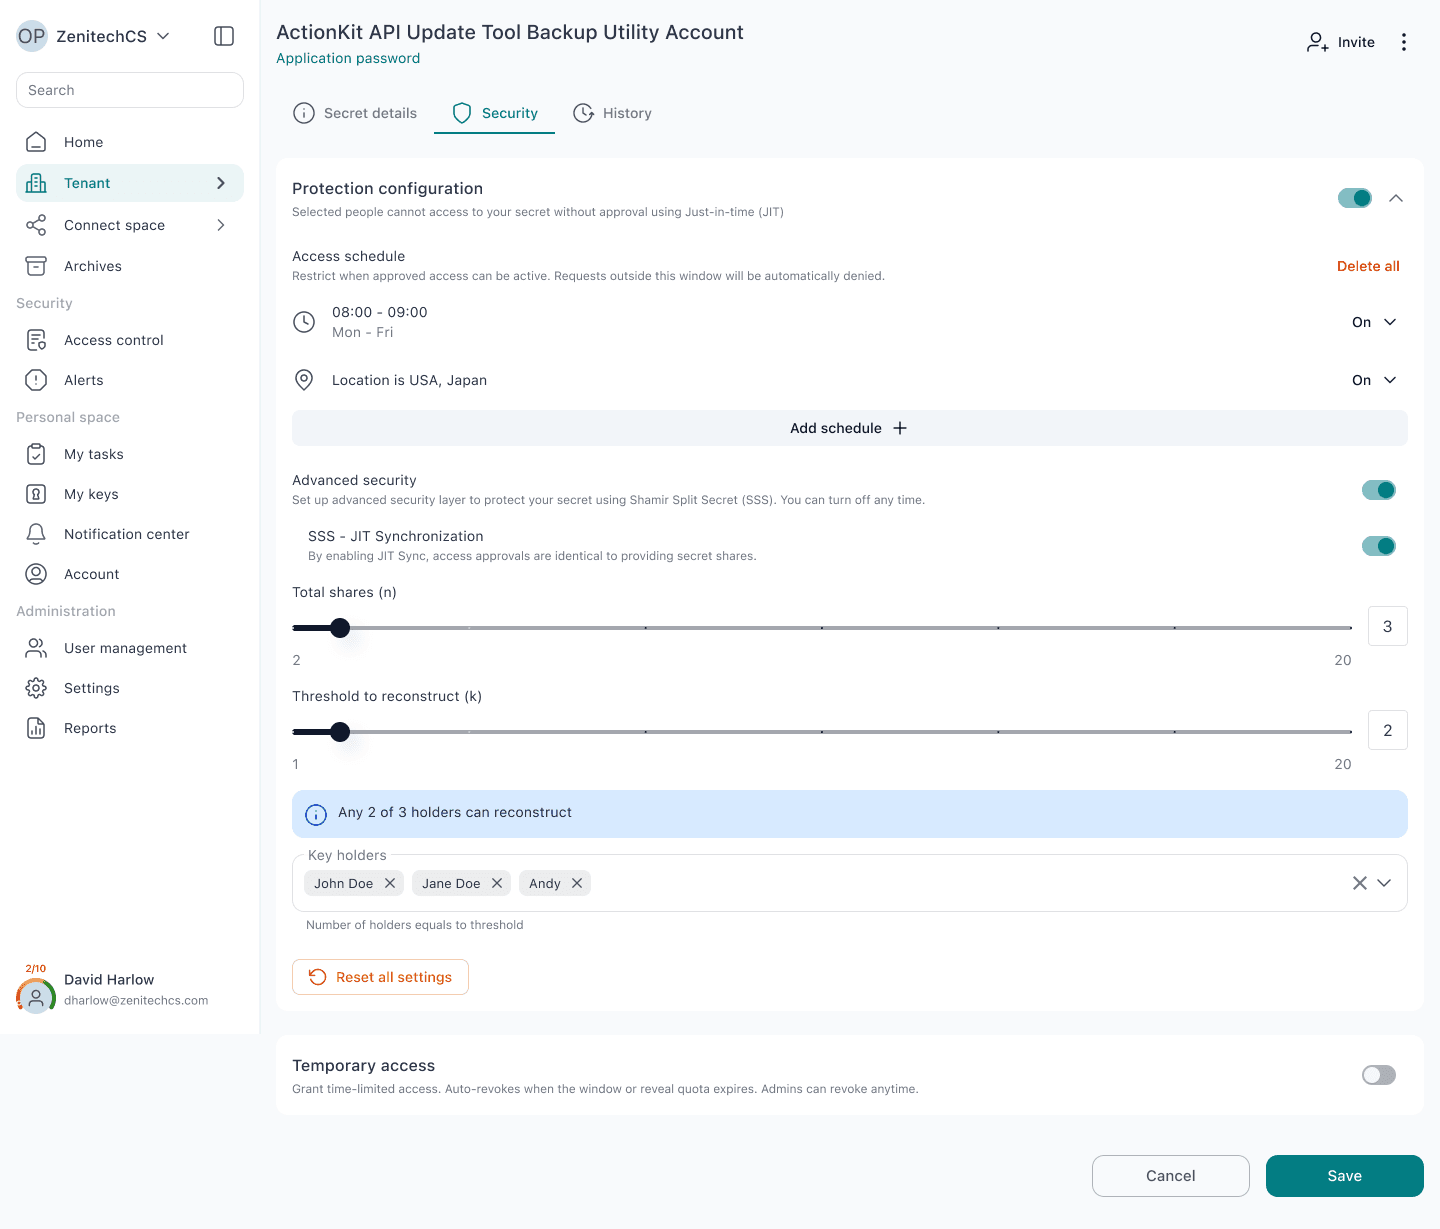
Eliminate standing privilege across both biological and synthetic identities. When an engineer needs production break-glass access or an AI agent executes an elevated remediation workflow, privileges are minted on demand, routed through multi-party human authorization, and bound to tight temporal windows. Every keystroke, API call, and autonomous mutation is captured in an immutable audit ledger, then torn down instantly upon completion. Neither your admins nor your agents keep a permanent foothold in mission-critical infrastructure.
Pricing
Simple, transparent pricing built for secure-first organizations. Start protecting your secrets in minutes.
Try TeamKey's zero-knowledge vault with a small team, no cost.
Advanced access controls and integrations for growing teams.
Enterprise-grade custom compliance and dedicated support.
End-to-end security
Your vault remains cloaked behind an SDP perimeter governed by self-maintaining context-aware policies that adapt to posture and trust in real time, while secrets remain encrypted under keys TeamKey never sees, stores, or transmits. Zero trust in the access model. Zero knowledge in the storage model.
99.999%
Designed for continuous high-availability operation across global regions.
<200ms
Ephemerally generated, high-velocity secrets injection that won't lag CI steps.
12
Audited environments to map your regulatory goals out of the box.
Tailored solutions for every team and use case.
Move fast without compromising on security.
Ship code with secrets managed automatically.
Enforce policies across your entire stack.
Manage multiple client environments securely.
Scale access governance across the org.
Purpose-built for the Draupnir ecosystem.
We'll send a quick note with next steps and a link to schedule time with our security team.